
For US Utilities serving 3,000-100,000 meters and for operations team, billing team and utility managers. For Heads of Billing who own collections accuracy and revenue leakage.
OT cybersecurity is the protection of the operational technology that runs physical equipment, such as the SCADA systems, controllers, pumps, and sensors that treat water or deliver power, from cyberattacks that could disrupt service or damage equipment. For utilities it sits alongside IT security, which protects business systems like billing and customer records, and cloud security, which covers the software and data a utility runs on a provider's infrastructure. The three are connected, so a utility's security plan has to cover all of them together.
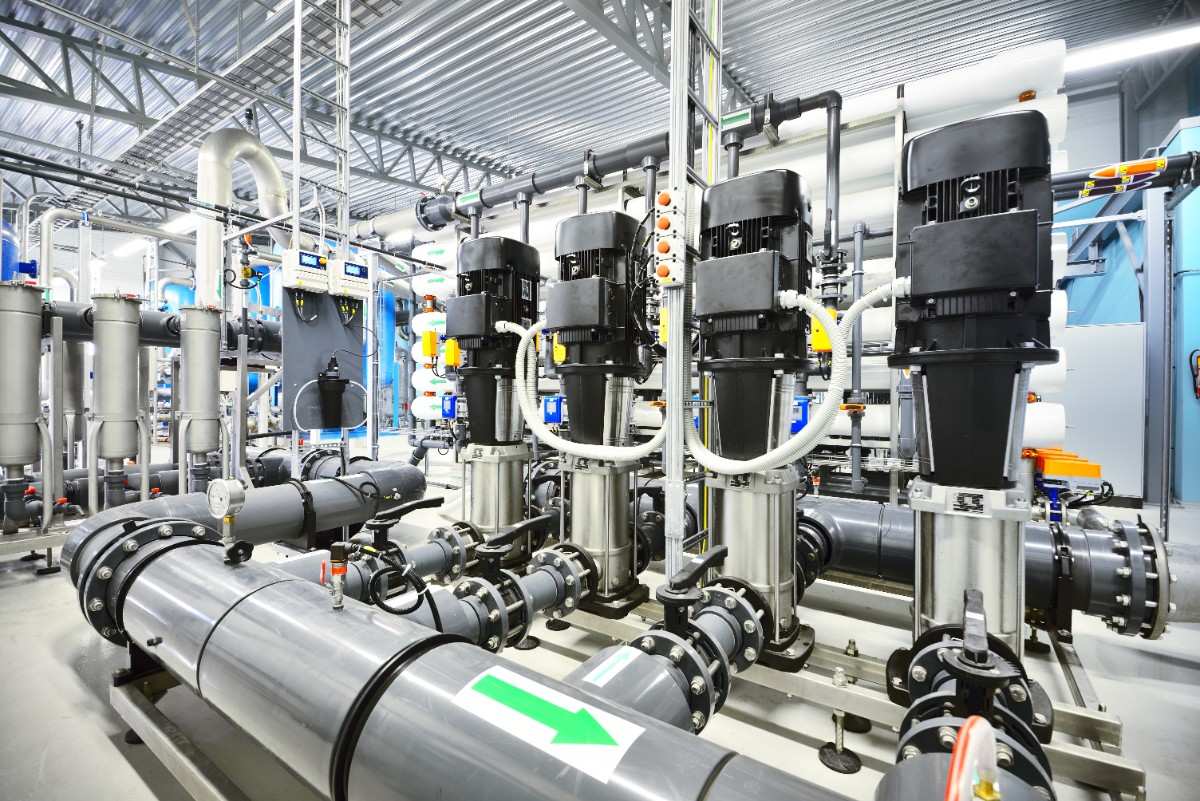
NIST defines operational technology as a broad range of programmable systems and devices that interact with the physical environment, detecting or causing a direct change through the monitoring and control of devices and processes (NIST SP 800-82 Rev. 3). At a utility, that means the systems that open valves, run pumps, switch circuits, dose chemicals, and read sensors: industrial control systems, SCADA, programmable logic controllers, and the networks that connect them.
OT cybersecurity is the practice of keeping those systems available, accurate, and under the utility's control. A breach of an OT system does not just expose data; it can change pressure in a water main, stop a treatment process, or cut power to customers. That is why safety and availability usually come first in OT security, ahead of confidentiality.
Utilities also run information technology: the business systems for billing, accounting, customer service, and records. The customer information system that holds accounts and bills is the most common example, and it is often the first system a utility moves to the cloud. IT and OT were once kept apart, but meter reads, work orders, and operational data now flow between them, so a weakness on one side can expose the other.
This guide expands on an episode of Bynry's Utility Cloud Guide podcast. Bynry founder Nilesh Gudhe talks with Kaiser Siyit, a cybersecurity specialist responsible for data and access security at a water utility, and Devesh Sinha, a senior consultant who works with utilities on process and technology change, about why utilities are exposed and how IT, OT, and cloud risk connect.
If the player does not load, watch Cybersecurity for Utilities: Managing Cloud, IT, and OT Risk on YouTube.
In the episode, Kaiser Siyit explains that IT and OT need different protection because they behave differently. Business servers are typically replaced every three to five years and have a large market of security tools, while some OT components stay in service for 20 to 30 years, come from specialized vendors, and have far fewer security products built for them.
Utilities face the same ransomware and fraud as any business, plus threats that most businesses do not. The factors that come up most often:
The riskiest point in most utility networks is where IT and OT connect. SCADA data feeds operations dashboards, AMI reads feed billing, and work orders move between field crews and office systems. Each connection is useful, and each needs to be deliberate.
Kaiser Siyit's advice in the episode is to keep a controlled gap between the two environments rather than letting them run as one network. In practice that means separating OT networks from business networks, limiting which systems can talk across the boundary, and passing data in one direction wherever possible.
Do you have a current map of every connection between your OT network and your business network?
Can any OT device be reached directly from the internet, including through a vendor's remote access tool?
If your billing system or email were compromised tonight, could an attacker reach a control system from there?
If the answer to any of these is unclear, the boundary between IT and OT is the first place to review.
Neither, by default. Both guests make the point that moving to the cloud changes who is responsible for which risks; it does not remove them. Devesh Sinha notes that the main concern utilities raise is losing visibility and control, while cloud platforms offer a larger security team and more mature monitoring than most small utilities can staff themselves.
Cloud providers describe this as a shared responsibility model: the provider protects the infrastructure that runs its services, and the customer remains responsible for items such as operating system patches, application settings, data, and access permissions, depending on the service used (AWS).
Identity is the control that matters most in the cloud. Kaiser Siyit points out that if a master administrator account is compromised, everything connected to it is exposed. Enforcing multi-factor authentication and reviewing who has administrator access are the highest-value steps for any cloud system. Our cloud vs. on-premise utility software comparison covers the wider trade-offs between the two models.
The guests describe a pattern that holds across most utilities: business systems move to the cloud first, while OT stays on site because it is physically tied to plants, pump stations, and substations.
Kaiser Siyit recommends treating a cloud move as a risk decision: record each risk in a register, decide which risks can be transferred to a provider and which the utility accepts, and match the decision to business goals. Our guide to migrating legacy utility systems to the cloud covers how utilities plan that move for business systems.
Devesh Sinha's central point in the episode is that security is a continuing process rather than a one-time project. The steps below combine that view with guidance from NIST, CISA, and EPA.
These steps match the priority actions EPA lists for water systems, which include reducing internet exposure, changing default passwords, inventorying OT and IT assets, maintaining incident response plans, backing up systems, and training staff (EPA).
In August 2025, CISA published Foundations for OT Cybersecurity: Asset Inventory Guidance for Owners and Operators with partners including EPA, NSA, and FBI. It describes an OT asset inventory as an organized, regularly updated list of an organization's OT systems, hardware, and software, and treats it as the starting point for a defensible architecture (CISA).
The guidance recommends defining scope, identifying assets through physical inspection and network surveys, organizing them in a taxonomy by function and criticality, keeping the data in a central system, and managing it through each asset's life. The priority attributes it lists include:
Kaiser Siyit makes the same point in the episode: an asset list should cover software, services, and people as well as hardware, because a utility cannot protect what it has not identified. Many utilities already hold part of this information in their asset management and GIS records, which makes a sensible starting point for the OT inventory.
Utilities do not have to invent a security program. Several public frameworks and rules set out what good practice looks like.
NIST released CSF 2.0 in February 2024, adding the Govern function and broadening the framework to all sectors rather than only critical infrastructure (NIST). NERC publishes its Critical Infrastructure Protection standards for entities that operate the bulk electric system (NERC). Compliance is still a gap for many water systems: EPA reported that over 70% of systems it inspected since September 2023 violated basic Section 1433 requirements (EPA).
Our cybersecurity guide for municipal utilities covers compliance obligations and governance from a utility director's point of view.
Most small and mid-sized utilities rely on outside help for part of their security program, and Kaiser Siyit recommends outsourcing expertise that is not available in-house. Two kinds of vendor matter: specialist OT security firms that assess and monitor control systems, and the software vendors whose cloud platforms hold utility data. For both, ask for evidence rather than assurances:
Devesh Sinha adds one more question: what is the vendor's own security culture? A vendor that trains its staff and monitors continuously is a stronger partner than one that treats compliance as a checklist.
SMART360 is not an OT security product. It does not protect SCADA systems, controllers, or field devices, and it is not a substitute for network segmentation or OT monitoring. It is a cloud-native utility management platform on the IT side: customer accounts, billing, payments, meter data, work orders, and asset records.
For utilities moving those business systems to the cloud, SMART360's security controls are documented on its security and compliance page:
Because SMART360 keeps asset records and meter data on the same platform, it can also hold part of the equipment information an OT asset inventory starts from. Our guide to utility CIS data security best practices covers the controls that protect customer data specifically.
OT cybersecurity is the protection of operational technology, the systems that monitor and control physical equipment such as SCADA, programmable logic controllers, pumps, valves, and sensors. For utilities, its first goal is keeping water and power services running safely, alongside protecting the data those systems produce.
IT security protects business systems and data, such as billing, finance, and email, which are updated often and have many security tools. OT security protects systems that control physical processes, which often stay in service for decades, cannot always be patched, and put service and safety at risk if attacked.
Published in August 2025 by CISA with EPA, NSA, FBI, and international partners, Foundations for OT Cybersecurity: Asset Inventory Guidance explains how owners and operators should build and maintain an organized, regularly updated list of their OT systems, hardware, and software, including which attributes to record for each asset.
Cloud software can be as secure as on-premise systems or more so, but it does not remove the utility's responsibilities. Under the shared responsibility model, the provider secures the infrastructure while the utility still manages user access, data, and how the system is configured. Multi-factor authentication and independent audit reports are the first things to confirm.
No. SMART360 is a cloud-native utility management platform for billing, customer information, meter data, work orders, and assets. It is SOC 2 Type II certified and uses encryption, multi-factor authentication, and exportable audit logs, but OT networks and control systems need dedicated OT security tools and practices.
Moving billing and customer systems to the cloud is a security decision as much as a technology one. SMART360 runs on AWS with SOC 2 Type II certification, encryption in transit and at rest, multi-factor authentication, and exportable audit logs, so utilities can modernize their business systems while keeping OT on its own protected network.
Bynry Inc.
8 The Green STE.R,
Dover, Kent,
Delaware 19901
+1 732-630-0285
Bynry Inc.
Serene Tower, Pakharbaug
Pune, Maharashtra 411021
+91 93252-51217